Car hacking: CAN bus, OBD-II, UDS y automotive attacks modernos
· 10 min de lectura
Los coches modernos tienen 50-100+ ECUs conectados por CAN bus, LIN, FlexRay. OBD-II expone bus a herramientas. Aprende el protocol stack automotive, UDS para diagnostics, ataques famosos (Miller-Valasek Jeep 2015, Tesla múltiples), y toolkit (CANtact, Kvaser, ICSim).
Los vehículos modernos son computers on wheels: 50-150 ECUs (Electronic Control Units) conectados por buses de comunicación (CAN bus predominante desde los 80s, FlexRay, LIN, y Ethernet automotive en modelos premium) controlando desde engine management hasta braking, infotainment, lane assist, autonomous driving features. El puerto OBD-II, obligatorio desde 1996 en coches sold en USA (resto del mundo poco después), expone acceso directo al CAN bus a cualquiera con un cable de 20 USD. Esto, combinado con connectivity (Bluetooth, WiFi, LTE/5G, V2X), ha hecho car hacking una área de research activa con implications de safety críticas.
Esta lección cubre el protocol stack automotive (CAN, UDS, DoIP), attack surface moderna (OBD-II, cellular, Bluetooth, keyless entry), casos famosos (Miller-Valasek Jeep 2015, múltiples Tesla research, Kia Boys 2022), y el toolkit básico (CANtact, CANable, Kvaser interfaces, ICSim simulator, python-can framework). Es la sexta lección de la Tanda 7, dedicada a especializaciones técnicas profundas.
Practica en own vehicles, simulators (ICSim), o authorized research programs. Modifying vehicles ajenos sin permission es damage property crime; dangerous modifications can injure/kill passengers.
Automotive protocol stack#
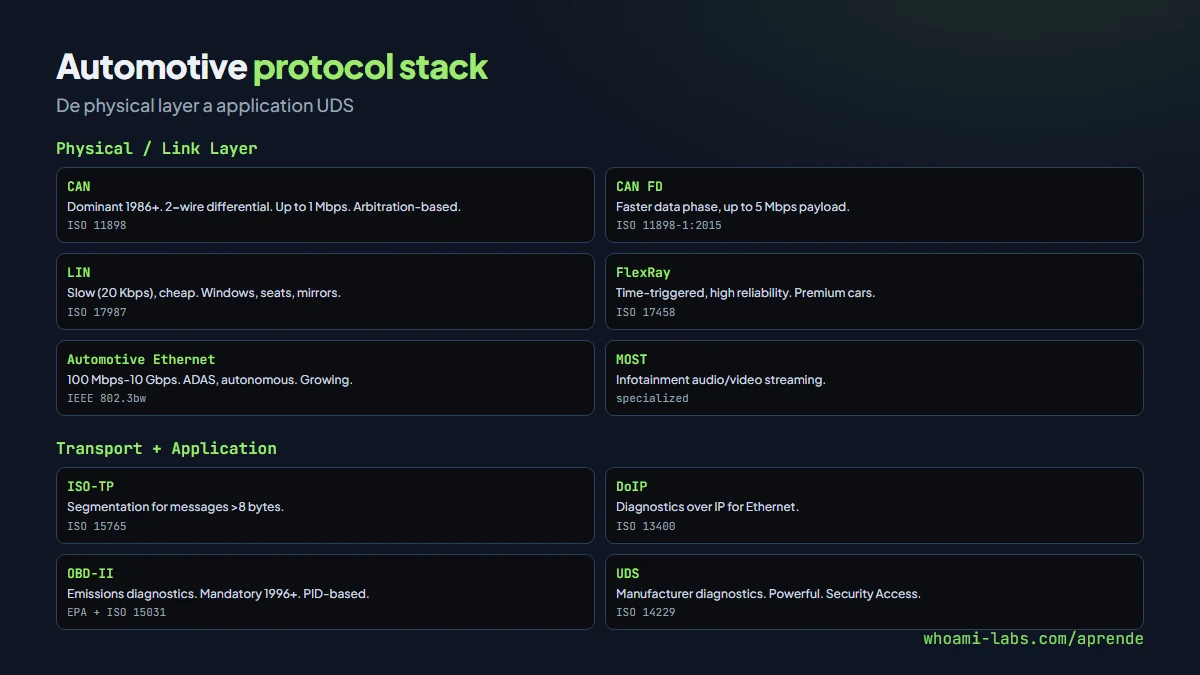
Layers from bottom to top:
Physical/link layer#
- CAN (Controller Area Network): dominant since 1986. 2-wire differential signaling, up to 1 Mbps. Arbitration-based (priority via ID).
- CAN FD: faster version, up to 5 Mbps payload.
- LIN (Local Interconnect Network): slow (20 Kbps), cheap. For windows, seats, mirrors.
- FlexRay: time-triggered, high-reliability. Premium cars.
- MOST (Media Oriented Systems Transport): for infotainment audio.
- Automotive Ethernet: 100 Mbps-10 Gbps. ADAS, autonomous. Growing adoption.
Transport/network#
- ISO-TP (ISO 15765): segmentation for messages larger than CAN frame (8 bytes).
- DoIP (Diagnostics over IP): over Ethernet.
Application#
- OBD-II: emissions diagnostics, standardized worldwide. PID-based.
- UDS (Unified Diagnostic Services, ISO 14229): manufacturer-specific diagnostics. Much more powerful than OBD-II.
- J1939: trucks and heavy vehicles.
OBD-II structure#
Standard port + connector in all cars. 16 pins. Common PID requests:
- 0x01 0x0D: vehicle speed.
- 0x01 0x0C: engine RPM.
- 0x09 0x02: VIN.
Anyone with OBD-II dongle (~20 USD) can read emissions data. More importantly, access CAN bus.
Attack surface moderna#
Growing with connectivity:
Physical access#
- OBD-II port: direct CAN access.
- USB ports: infotainment systems.
- SD card slots: firmware updates often loaded.
- Internal wiring: tap specific CAN buses behind panels.
Local wireless#
- Bluetooth: phones, keys, OBD dongles.
- WiFi: entertainment systems, hotspots.
- Keyless entry: relay attacks (amplify key fob signal, car thinks owner nearby).
- Rolling code attacks: RollJam-style capture + replay.
Cellular / long-range#
- Telematics: cellular modem in-car. Remote diagnostics, OTA updates.
- Companion apps: smartphone apps control vehicle features. API endpoints as attack surface.
- V2X (Vehicle-to-Everything): emerging 5G-based.
Supply chain#
- Infotainment components: often outsourced. Vulnerabilities inherited.
- Firmware update servers: compromise vendor cloud, push malicious updates.
Casos famosos#
Miller-Valasek Jeep hack (2015)#
Charlie Miller + Chris Valasek demonstrated remote compromise 2014 Jeep Cherokee:
- Attack vector: Uconnect cellular connection.
- Chain: exploit remote service → code execution infotainment → pivot via microcontroller to CAN bus → send CAN messages controlling steering, brakes, acceleration.
- Chrysler recalled 1.4M vehicles. Established car hacking as serious.
Tesla múltiples#
Pwn2Own Automotive tiene Tesla target repeatedly:
- 2019: pair found exploit chain winning $35k + Tesla Model 3.
- 2023: multiple vulnerabilities discovered, major rewards.
- Tesla generally responds quickly with OTA patches.
Kia Boys (2022-2023)#
TikTok viral trend exploiting missing immobilizers en certain Kia/Hyundai models. USB cable + screwdriver stole cars. Massive insurance crisis. Manufacturers reluctantly adding retrofits.
Keyless entry relay attacks#
Multiple researchers: amplify key fob signal across distance, car unlocks though key far away. Affects most brands. Mitigation: motion-sensing fobs disabling when still.
Toolkit#
Hardware interfaces#
- CANtact (Eric Evenchick): $70 USB-CAN interface. Beginner-friendly.
- CANable / CANtable: open source, affordable.
- Kvaser: professional, more expensive, reliable.
- PEAK PCAN: industry standard.
- Comma.ai Panda: multi-bus, popular in auto research.
Software#
- python-can: standard Python library for CAN.
- SocketCAN (Linux): kernel-level CAN support.
cansend,candump,cangen. - SavvyCAN: GUI for CAN analysis + reverse engineering.
- Caring Caribou: UDS exploration tool.
- ICSim: simulator for practicing without hardware.
Simulator-based learning#
ICSim includes:
- Virtual dashboard with speedometer, turn signals, doors, lights.
- Virtual CAN bus.
- Lets students replay/manipulate CAN messages.
- No vehicle required.
Comandos básicos#
# Linux SocketCAN with physical interface
sudo ip link set can0 up type can bitrate 500000

# Dump traffic
candump can0

# Send message
cansend can0 123#DEADBEEF

# Replay
canplayer -I capture.log

# Python
import can
bus = can.Bus('can0', bustype='socketcan')
msg = can.Message(arbitration_id=0x123, data=[0xDE, 0xAD, 0xBE, 0xEF])
bus.send(msg)
Basic enough for first experiments.
UDS exploration#
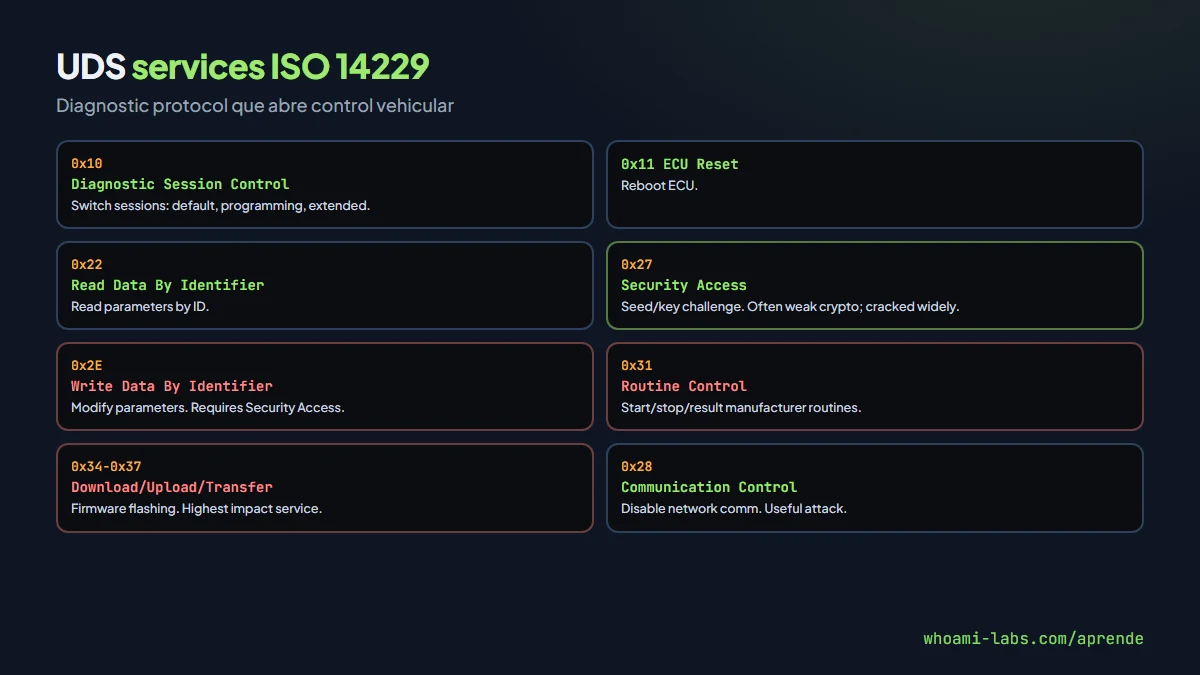
UDS provides rich diagnostic services. Many manufacturer-specific. Services include:
- 0x10 Diagnostic Session Control: switch sessions (default, programming, extended).
- 0x11 ECU Reset: reboot ECU.
- 0x14 Clear Diagnostic Information: erase trouble codes.
- 0x22 Read Data By Identifier (RDBI): read parameters.
- 0x27 Security Access: unlock advanced functions via seed/key challenge.
- 0x28 Communication Control: disable network communication.
- 0x2E Write Data By Identifier (WDBI): write parameters.
- 0x31 Routine Control: start/stop/result routines.
- 0x34-0x37 Download/Upload/Transfer Data: firmware flashing.
Security Access (0x27) typically weak cryptography, often cracked. Allows access to WDBI, Routine Control, Reprogramming. Researchers extract firmware, modify, reflash en authorized engagements.
Defensive side#
Industry improving slowly:
- Message authentication (AUTOSAR SecOC): HMAC on CAN messages.
- Gateway ECUs: segment buses, filter messages.
- IDS/IPS automotive: anomaly detection on CAN traffic.
- Secure boot + signed firmware.
- Hardware security modules (HSM) en ECUs premium.
- Regulatory pressure: UN R155 (cybersecurity) + R156 (software updates) effective 2024+.
Still inconsistent across industry. Lower-cost vehicles lag luxury.
Entry en careera#
Automotive security pathway:
- Learn CAN basics (python-can, SocketCAN).
- Buy OBD-II dongle + own car (consult service manual, don't break car).
- ICSim practice.
- CTF challenges (DefCon Car Hacking Village).
- Networking at BlackHat Automotive, Escar.
- Entry roles: automotive OEM security teams, Tier 1 suppliers (Bosch, Continental), specialized consultancies.
Salaries competitive. Growing market. Shortage of talent com combinación automotive + security.
Walkthrough: ICSim básico#
Para fijar práctica sin hardware, ICSim provides full simulator.
Setup:
git clone https://github.com/zombieCraig/ICSim
cd ICSim && make

# Setup virtual CAN
sudo modprobe vcan
sudo ip link add dev vcan0 type vcan
sudo ip link set up vcan0

# Run simulator
./icsim vcan0 &
./controls vcan0
Dashboard appears + control panel. Explore CAN traffic:
candump vcan0 | head
# Many messages, varying IDs y data
Identify speedometer:
- Press up arrow en controls (accelerate).
- Observe
candumpoutput. - Messages for speed should change proportionally.
- Correlate ID + bytes.
Replay attack:
# Capture 10 seconds
timeout 10 candump -l vcan0

# Replay
canplayer -I candump-2026-xxxx.log
Watch speedometer behavior. Control acceleration via replay.
Spoofing:
# Send bogus message
cansend vcan0 244#00000000AABB
Craft specific bytes to display specific speed. Classic car hacking exercise.
ECUs específicas#
Common ECUs per vehicle:
- Engine Control Module (ECM/PCM): engine management.
- Transmission Control Module (TCM): gearbox.
- Body Control Module (BCM): windows, lights, locks.
- Instrument Cluster: dashboard.
- Infotainment Head Unit (IHU): entertainment.
- ADAS modules: lane assist, cruise control.
- Gateway ECU: bus segmentation, routing.
- Telematics Control Unit (TCU): cellular connectivity.
Each ECU: firmware + CAN communication + diagnostic interface. Attack chain often jumps between ECUs.
Regulación#
Automotive security regulation accelerating:
- UN R155: cybersecurity management system (CSMS). Required for type approval en many markets 2024+.
- UN R156: software update management system (SUMS). Secure OTA mandatory.
- ISO/SAE 21434: cybersecurity engineering standard.
- ISO 24089: software update engineering.
Manufacturers must implement SIRTs, incident response, continuous security monitoring. Tier 1 suppliers cascading requirements. Industry transforming rapidly.
Preguntas frecuentes#
¿Es ilegal CAN bus analysis?#
Own vehicle: generally legal con caveats (EPA emissions). Rental/leased unclear. Modifying systems safety-critical risky legally.
¿Qué coche para learning?#
Older Ford/Toyota (2010-2018) han well-documented CAN. Modern Teslas have interesting features pero highly restricted por manufacturer.
¿Keyless entry mitigation?#
Faraday bag for fob at home. Vendor retrofit motion-sensing. Steering wheel lock classic but effective complement.
¿Autonomous driving security?#
Growing concern. Sensor spoofing (lidar, camera), AI adversarial attacks, decision manipulation. Research area hot.
¿V2X security?#
Emerging. 5G-based vehicle-to-infrastructure communication. Public key cryptography en V2X messages. Still deploying.
¿Dónde practico?#
El laboratorio armageddon de whoami-labs incluye ICSim deployment con simulated vehicle CAN bus. Practica sniffing, replay, UDS exploration without hardware physical requirement.
Resumen#
- Vehículos modernos = 50-150 ECUs conectados CAN bus (+ LIN, FlexRay, Ethernet).
- OBD-II: standard port, exposes CAN. Attack surface entry point.
- UDS (ISO 14229): powerful diagnostic protocol. Security Access often weak.
- Casos: Miller-Valasek Jeep 2015, Tesla Pwn2Own múltiples, Kia Boys 2022.
- Attack surface: OBD-II, Bluetooth, cellular telematics, companion apps, keyless entry.
- Toolkit: CANtact ($70), SocketCAN Linux, python-can, ICSim simulator.
- Defense: AUTOSAR SecOC, gateway ECUs, UN R155 regulation 2024+.
Industry trends 2026#
Direction:
- Software-defined vehicles: ECU consolidation, Linux/QNX dominant. Firmware updates sophisticated.
- Automotive Ethernet: 10 Gbps backbones replacing CAN for high-bandwidth.
- Zonal architectures: zone controllers aggregating local ECUs. Simplifies wiring.
- Over-the-air updates universal: safety-critical ECUs updatable remotely.
- AI/ML in vehicles: driving, infotainment. New attack surfaces.
- V2X deployment: 5G-based communication rolling out slowly.
Automotive security market growing rapidly. Shortage of automotive + security talent. Entry roles accessible, senior positions competitive.
Impact social#
Car hacking concerns transcend technical:
- Safety-critical: unlike most security bugs, consequences can be fatal.
- Scale: millions of vehicles share platforms. Single vuln massive.
- Longevity: cars last 10-20 years. Legacy security problem persistent.
- Public policy: regulation struggling to keep pace.
- Consumer awareness: limited; buyers don't evaluate security.
Responsible disclosure particularly important. Vendors slow to patch historically. Research coordinated with safety considerations primary.
Resources para profundizar#
Comunidad automotive security:
- Open Garages: community garages focused on security research.
- Hackaday Automotive: regular coverage.
- IOActive: consultancy pioneering car hacking research.
- Automotive Security Research Group (ASRG): professional community.
- Car Hacking Village (DefCon): annual gathering.
- Escar Conference: embedded security + automotive.
- BlackHat Automotive: enterprise track.
Networking imprescindible; community small pero active. Mentorship common for serious entrants.
Herramientas commercial#
Beyond open source, commercial platforms:
- VehicleSpy (Intrepid Control Systems): CAN analysis professional.
- CANoe (Vector): industry standard simulation.
- ICSProgrammer: UDS reflashing.
- NSG for UDS: comprehensive UDS testing.
- PlaxidityX (ex Argus): automotive IDS.
Enterprise engagements often require these. Entry-level learners start con open source, graduate to commercial.
Autonomous driving security#
Emerging area specifically:
- Sensor security: lidar spoofing, camera adversarial attacks demonstrated academic papers.
- ML model attacks: adversarial examples causing misclassification (stop sign → speed limit).
- Sensor fusion vulnerabilities: multiple sensors agreeing adversarial input.
- Decision manipulation: fuzz L4 driving decisions.
- V2X trust: communicated info could be malicious.
Research pioneered by universities (CMU, UC Berkeley). Vendor investment growing. Still early.
Autonomous vehicles roll out gradually; security practices mature same pace. Expect sustained research + regulatory attention next decade con inversión significativa sostenida desde actores grandes diversos del sector automotriz mundial en expansión creciente constante hacia nuevas capacidades técnicas y comerciales.
Careers automotive security#
Growing demand:
- OEM security teams: Tesla, Ford, GM, Toyota, VW have teams.
- Tier 1 suppliers: Bosch, Continental, Denso, Delphi.
- Specialized consultancies: IOActive, Argus/PlaxidityX, Karamba Security, GRIMM.
- Regulatory bodies: CISA automotive sector, NHTSA Vehicle Research.
- Academic research: funded industry + government.
Salaries 100k-200k USD senior typical. Specialization + automotive domain knowledge commands premium. Entry via general security + automotive learning, or vice versa.