OSINT avanzado: geolocation forense, SOCMINT, dark web monitoring
· 11 min de lectura
Aprende técnicas avanzadas de OSINT: geolocation de imágenes (shadows, EXIF, landmarks), SOCMINT en redes sociales, dark web monitoring, verification protocols. Base para threat intel, investigations y journalism.
OSINT (Open Source Intelligence) avanzado va mucho más allá de Google dorks y búsquedas en LinkedIn. Incluye disciplinas especializadas como geolocation forense (identificar locations específicas de fotos sin metadata), SOCMINT (Social Media Intelligence) con tools dedicadas para análisis de redes, dark web monitoring para identificar brechas de datos tempranas, imagery analysis con satélite y plataformas de mapping, y verification protocols para distinguir fuentes confiables de misinformación. En 2026 OSINT es disciplina establecida con profesionales dedicados, usada por threat intel teams, periodistas investigativos (Bellingcat siendo el ejemplo canónico), law enforcement, y recruiters.
Esta lección cubre el toolkit moderno de OSINT avanzado, métodos de verification, y aplicaciones ofensivas (reconnaissance pre-engagement) y defensivas (threat intel). Es la penúltima lección de la Tanda 6.
OSINT uses public information exclusively. Nothing en esta lección involves unauthorized access. Pero privacy considerations, legal frameworks (GDPR), y ethics apply.
Las disciplinas de OSINT#
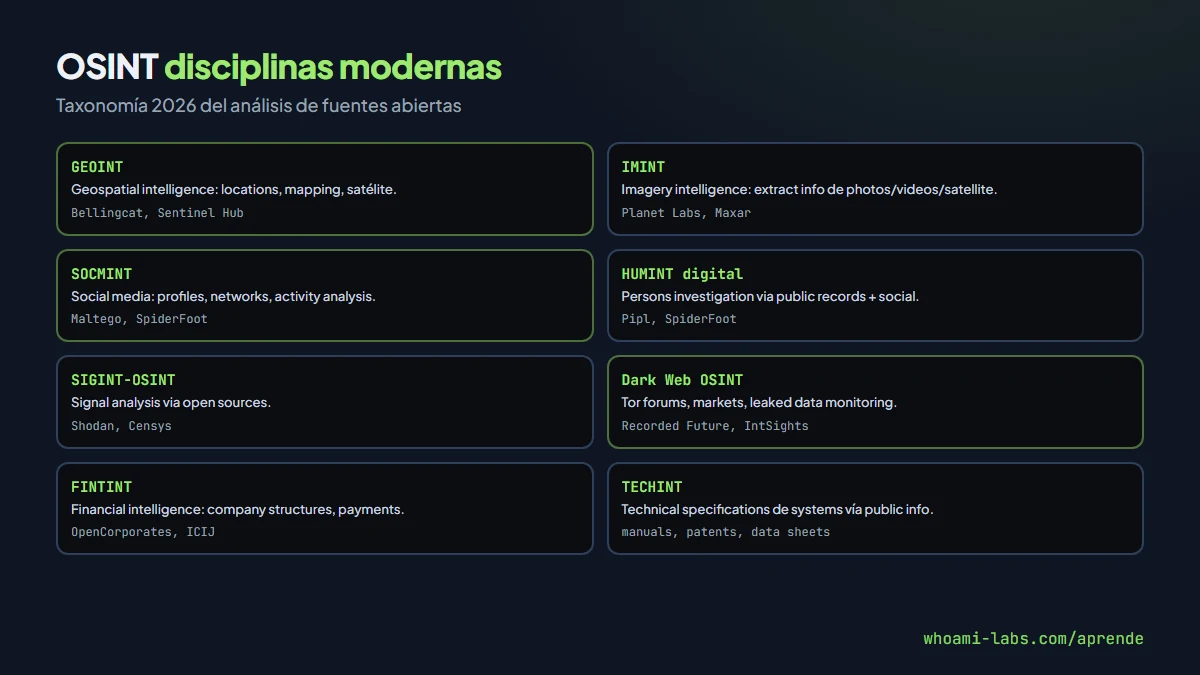
Taxonomía OSINT moderna:
- GEOINT (Geospatial Intelligence): locations, mapping, satellite.
- IMINT (Imagery Intelligence): analysis de imágenes para extract información.
- SOCMINT (Social Media Intelligence): profiles, networks, activity analysis.
- HUMINT digital: personas investigation vía public records.
- SIGINT-OSINT: signal analysis via open sources (Shodan, Censys).
- Dark Web OSINT: monitoring forums, markets, leaked data.
- FINTINT (Financial Intelligence): company structures, transactions públicos.
Cada uno tiene tools y techniques específicos.
Geolocation forense#
Identificar location exacta de foto sin metadata EXIF. Técnicas de Bellingcat canonical:
Shadows analysis#
Dirección + longitud de sombras + hora del día aproximada + época del año = latitude estimable. Websites como suncalc.org calculan positions solares.
Landmarks identification#
- Edificios específicos.
- Street signs (idioma, tipografía regional).
- License plates patterns.
- Business signage (local chains).
Google Street View, Yandex Maps (strong en Rusia/Asia Central), Baidu Maps (China) para verification.
Vegetation / terrain#
- Biomes específicos.
- Agricultural patterns.
- Mountain silhouettes matchable con topo maps.
Weather / season#
- Snow, foliage type, sun angle informs date range.
Reflections#
- Reflections en windows, puddles reveal otros angles.
Audio analysis#
- Si video, accents, languages, specific sounds (church bells, specific alarm types).
Tools canonicos:
- Google Earth Pro (free) + Street View.
- Yandex reverse image search: mejor que Google para específicos.
- TinEye: image provenance.
- Mapillary: crowdsourced street-level imagery.
- Overpass Turbo: OpenStreetMap complex queries.
- Sentinel Hub: satellite imagery.
SOCMINT#
Investigation profiles redes sociales para research, threat intel, due diligence.
Tools específicos#
- Maltego: link analysis platform. Visual graphs de relationships. Puede ingest multiple OSINT sources.
- SpiderFoot: OSINT automation framework.
- Social Analyzer: AI-based username search across platforms.
- Sherlock / Snoop: username enumeration.
- OSINT Industries: paid platform para corporate investigations.
Patterns de investigation#
- Cross-reference profiles con mismo username / email.
- Analyze posting patterns (timezones, activity).
- Identify connections network (who follows who).
- Historical data via Wayback Machine archive.
- Reverse search profile photos (TinEye, Yandex).
Platforms coverage#
- LinkedIn: profesional network, great for corporate recon.
- Twitter/X: real-time, locations, communities.
- Instagram: photos (métadata often stripped pero captions contain info).
- Facebook: harder today por privacy settings.
- TikTok: emerging para younger demographics.
- Discord/Telegram: communities-based, invite links accessible sometimes.
Dark web OSINT#
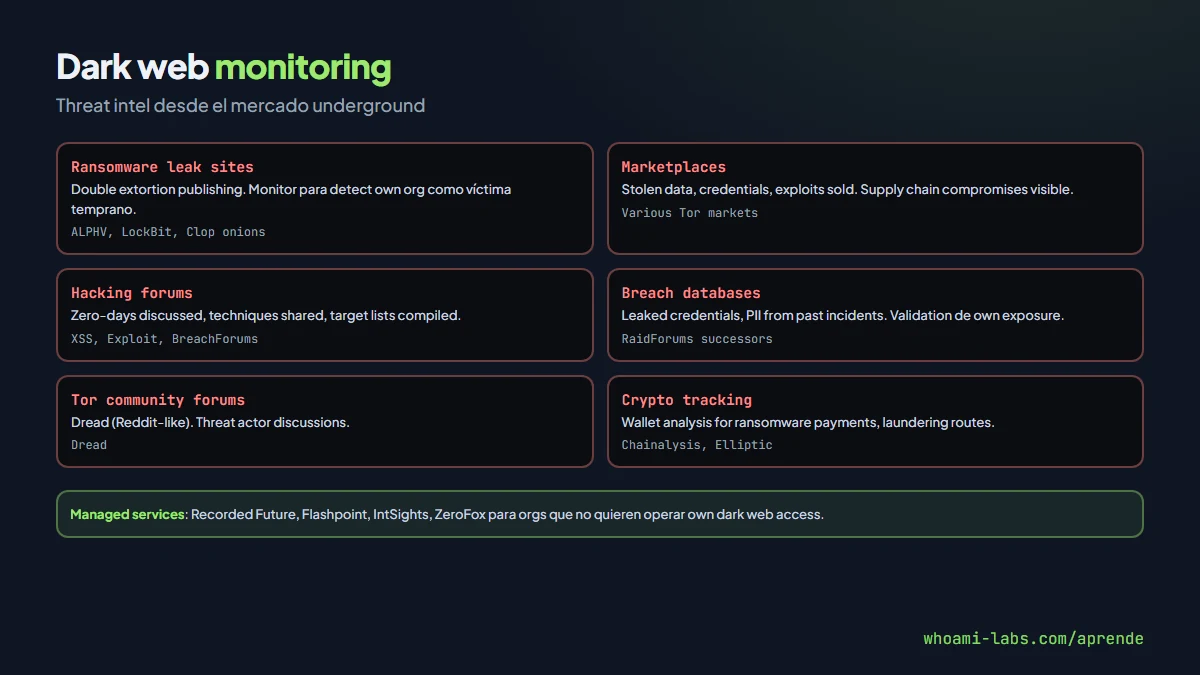
Monitor dark web para threat intel:
Access#
- Tor Browser para onion sites.
- i2p, Freenet alternative networks.
- Comercial services (Recorded Future, Flashpoint) aggregate without needing own access.
Qué monitorear#
- Ransomware leak sites: double extortion publication.
- Marketplaces: stolen data, credentials sold.
- Hacking forums: zero-days, techniques, target lists.
- Breach databases: paste sites (less anymore after takedowns).
- Crypto tracking: wallet analysis.
Tools#
- OnionScan: analysis de onion sites.
- AhMia: Tor search engine.
- Dread: Reddit-like Tor forum para community monitoring.
- Grayhat Warfare: bucket enum (cross-reference con cloud lesson).
Legal considerations#
Pasive observation OK. Active engagement (buying data to verify) peligroso legally. Many jurisdictions criminalize dark market purchases incluso para research.
Para empresas: use managed services (Recorded Future, ZeroFox) que abstract complexity.
IMINT: imagery analysis#
Satellite imagery analysis para investigations:
Sources#
- Google Earth Pro: historical imagery, measure tools.
- Sentinel Hub (ESA): free Copernicus satellite data.
- Planet Labs: high-resolution, commercial.
- Maxar: highest resolution (classified-grade available comercial).
Techniques#
- Change detection: comparing images over time.
- NDVI (vegetation index): agricultural analysis.
- Thermal imagery: night, cloud-cover.
- SAR (Synthetic Aperture Radar): see through clouds, nighttime.
Use cases#
- Infrastructure monitoring: new construction suggesting intelligence targets.
- Traffic analysis: port, border activity.
- Agricultural: supply chain disruption prediction.
- Environmental: deforestation, pollution tracking.
- Military movements: equipment, infrastructure changes.
Verification protocols#
Critical en OSINT: verify sources + information:
Methods#
- Cross-reference multiple independent sources.
- Reverse image search para image provenance.
- Weather / astronomical checks para match claimed time/location.
- Linguistic analysis: dialect, spelling matching claimed origin.
- Technical metadata: EXIF, file analysis.
- Human verification: domain experts.
Bellingcat methodology#
Emilio Rodriguez et al. established rigorous methodology:
- Document every step.
- Preserve evidence.
- Transparent sourcing.
- Peer review before publication.
- Correction protocols.
Public archive investigation reports como demonstration.
Ethics y legal#
Ethics#
- Privacy: individuals vs public figures different standards.
- Harm: investigation causing real harm → avoid unless clear public interest.
- Attribution: avoid definitive claims sin very strong evidence.
- Minors: extra care.
- Victims: respect, re-victimization avoidance.
Legal#
- GDPR (EU): data about EU residents highly regulated. Legitimate interest basis required.
- CCPA (California): similar protections.
- Honduras / various: varying levels.
- Journalist exemptions vary by jurisdiction.
Corporate OSINT programs typically have legal counsel involvement y data handling policies.
Herramientas y platforms#
Compilation canónico:
- OSINT Framework (osintframework.com): comprehensive directory.
- Bellingcat Online Investigation Toolkit: curated tools.
- Maltego CE: community edition free.
- SpiderFoot HX: paid tier.
- recon-ng: Python framework modular.
- Shodan, Censys: internet-connected device search.
- Have I Been Pwned: breach data.
- DNSDumpster: DNS reconnaissance.
- crt.sh: certificate transparency logs.
Para threat intel comercial: Recorded Future, Flashpoint, DomainTools, IntSights, ZeroFox.
Walkthrough: investigation ejemplo#
Para fijar el patrón, Bellingcat-style investigation methodology aplicada:
Caso ficticio: foto en social media muestra evento presuntamente en Berlín. Verify.
Paso 1 - Image analysis:
- EXIF metadata removed? Expected en modern platforms.
- Visual landmarks: building architecture, street signs, cars.
- Idioma de signs: Alemán confirma región.
- Vehicles license plates patterns: Berlin pattern starts with B.
Paso 2 - Shadow analysis:
- Shadow direction + length + sun position → approximate time of day.
- suncalc.org con estimated date (from posting metadata) confirms possible sun position en Berlín latitude.
Paso 3 - Weather / season:
- Clothing visible matches posting date's weather.
- Vegetation state matches reported season.
Paso 4 - Specific location:
- Street View exploration en area probable.
- Match specific buildings, intersection.
- Confirmed: Alexanderplatz area.
Paso 5 - Cross-verification:
- Other posts same event?
- News reports confirm event occurred that date/location?
- Multiple sources corroborate?
Paso 6 - Document:
- Preserved images, screenshots.
- Documentation chain.
- Peer review.
Paso 7 - Publication: solo si evidence overwhelming y public interest justifies.
OSINT en corporate threat intel#
Para equipos de threat intel empresariales, OSINT structure:
- Dedicated analysts monitoring specific threats.
- Platforms (Recorded Future, Flashpoint) aggregate feeds.
- Internal integration con SIEM, SOAR.
- Reports regulares para executive leadership.
- Attribution workshops cross-industry para collective defense.
Capability maturation: entry-level analyst → senior → lead threat intel architect. Salaries competitive, strong hiring 2024-2026.
Errores comunes#
- Jumping a conclusions sin verification.
- Mistaking similar-looking info como same person.
- Trusting translated content sin native speaker verification.
- Ignoring cultural context.
- Oversharing findings (OpSec para investigator).
- Not preserving evidence properly.
Preguntas frecuentes#
¿OSINT es «hacking»?#
Technically no. Uses only public info. But intersects (recon pre-pentest, etc.).
¿Cómo empezar carrera OSINT?#
Participate en challenges (Trace Labs CTFs), writeups Bellingcat, follow experts on Twitter, specific courses (SANS SEC487, OSINT Combine).
¿Legal diferentes jurisdictions?#
Yes significantly. EU, Canada stricter que US. Journalism protections. Check local attorney if operating cross-border.
¿OSINT para employment background checks?#
Legally gray zone. Many jurisdictions regulate pre-employment screening. HR teams necesitan legal advice, specialized services.
¿Dark web access es legal?#
Usually yes just for access. Market purchases, drug deals clearly illegal. Verify local law.
¿Dónde practico?#
El laboratorio orion-recon de whoami-labs incluye simulated OSINT challenges: geolocation puzzles, SOCMINT investigations, dark web monitoring scenarios. Practicas methodology y verification protocols en setting controlado.
¿Vale la pena OSINT certs?#
SANS SEC487 (OSINT), OSINT Combine certifications, TraceLabs reputation points. Writeups públicos y participation en Trace Labs CTFs tienen mucho más weight que certs para employers OSINT-specific.
¿AI cambia OSINT?#
Yes significantly. LLMs analyzing massive texts, image recognition identifying faces/places, deepfakes complicating verification. Both offensive (automation) y defensive (deepfake detection). Field evolving rápidamente.
¿Como protect against OSINT about me?#
- Minimize social media presence.
- Privacy settings aggressive.
- Different usernames across platforms.
- No metadata in posted images.
- Review via Have I Been Pwned, Pentester Framework personal.
¿OSINT vs SIGINT vs HUMINT ethical lines?#
OSINT only public info. SIGINT intercepts communications (government typically). HUMINT uses sources (spying). Very different legal frameworks y ethics.
¿Trace Labs CTFs legal?#
Yes. Non-profit, missing persons focus. Participation builds portfolio y helps real investigations. Platform reconcoized by law enforcement.
¿Ecosystem de tools evolving?#
Rápidamente. Follow @OSINTtechniques, @IntelTechniques, @bellingcat on Twitter/Mastodon. Communities activas en Reddit r/OSINT.
Resumen#
- OSINT disciplinas: GEOINT, IMINT, SOCMINT, HUMINT, dark web OSINT.
- Geolocation forense: shadows, landmarks, Yandex + Street View + Mapillary.
- SOCMINT: Maltego, SpiderFoot, cross-reference profiles.
- Dark web: Tor markets, ransomware sites, breach databases. Legal considerations.
- IMINT: Sentinel Hub (free), Planet Labs, Maxar para high-res.
- Verification: Bellingcat methodology, multiple sources, metadata.
- Legal: GDPR, privacy, journalist exemptions vary por jurisdicción.
Bellingcat como referencia industria#
Bellingcat, fundada por Eliot Higgins en 2014, es organización no-profit que revolucionó investigative journalism via OSINT. Casos famosos:
- MH17 downing (2014): identified Buk missile launcher y Russian military unit.
- Skripal poisoning (2018): traced GRU officers via public records y travel.
- Khashoggi murder investigation (2018): Saudi hit squad members.
- Ukraine conflict (2022+): continuous investigation, equipment tracking, atrocity documentation.
- Various financial corruption cases.
Methodology público, courses offered, large community impact. Para aspirantes OSINT, estudiar casos Bellingcat es essential. Industry standard-setting.
Convergencia AI y OSINT#
En 2026, AI integrates increasingly:
- Face recognition (Clearview, PimEyes) ethically controversial pero widely used.
- Deepfake detection: tools para verify authenticity.
- Translation: real-time acceleration investigations.
- Image clustering: find similar across platforms.
- Pattern recognition: identify bot networks.
- Automated monitoring: continuous feeds analysis.
Trade-off: AI accelerates but introduces errors. Human verification remains essential. Field balancing capability con responsibility.
Rol profesional emergente#
OSINT como carrera dedicada ha madurado:
- Dedicated OSINT roles en threat intel teams.
- Consultoría especializada para corporate investigations, M&A due diligence.
- Journalism (Bellingcat, Lighthouse Reports, Al Jazeera investigations unit).
- Law enforcement OSINT units en police departments.
- Private investigators usando OSINT methodology.
- Insurance investigations verifying claims via OSINT.
Salaries range widely por sector. Public interest journalism paga less que corporate consulting. Mid-career practitioners con solid portfolio comando premium rates especially para high-stakes investigations específicas en contextos sensibles con clientes corporativos regulados.
Entry path típico: participate CTFs (Trace Labs), publish writeups, join professional community (OSINT Curio, OSINT Combine community), build portfolio demonstrating methodology. Formal certs matter less que demonstrated skill en el campo práctico real de la disciplina OSINT global en expansión actual.
Es una disciplina que combina curiosidad intelectual, paciencia metódica, y responsabilidad ética en proporciones aproximadamente iguales durante la práctica profesional diaria del analista profesional especializado en el campo contemporáneo.